Catch Vulnerabilities before
Attackers do.
AuditGate continuously monitors your APIs, detects security flaws, and helps you fix them before they become costly security breaches.
Secure your APIs at every stage
Catch vulnerabilities early in development, validate fixes at deploy, and continuously monitor runtime behavior, so your APIs stay secure from the first commit to production.
Real-time Monitoring
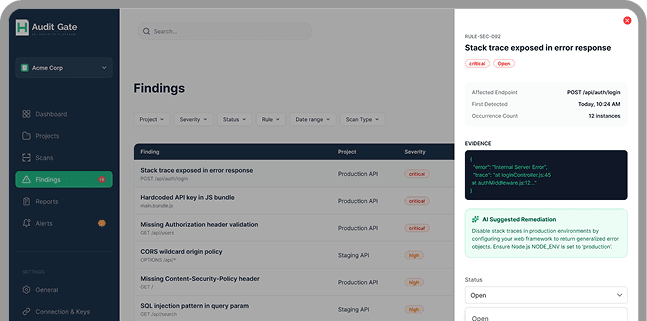
Watch findings appear the moment they are detected. Every request through your API is inspected live, with the severity, the evidence and the affected endpoint attached to each result.
Vulnerabilty Detection
Scan OpenAPI definitions and endpoints early in development, and configure scans to run automatically with every staging deploy.
Compliance Reports
Instantly generate audit-ready security reports structured against SOC 2 and PCI-DSS control areas.
CI/CD Pipeline Integration
Catch issues at the build stage, not after the incident. Fast checks. Zero slowdown. Clean deploys.
Team Collaboration
Assign vulnerabilities directly to developers, discuss remediation steps, and track resolution inside the console.
Health Score Tracking
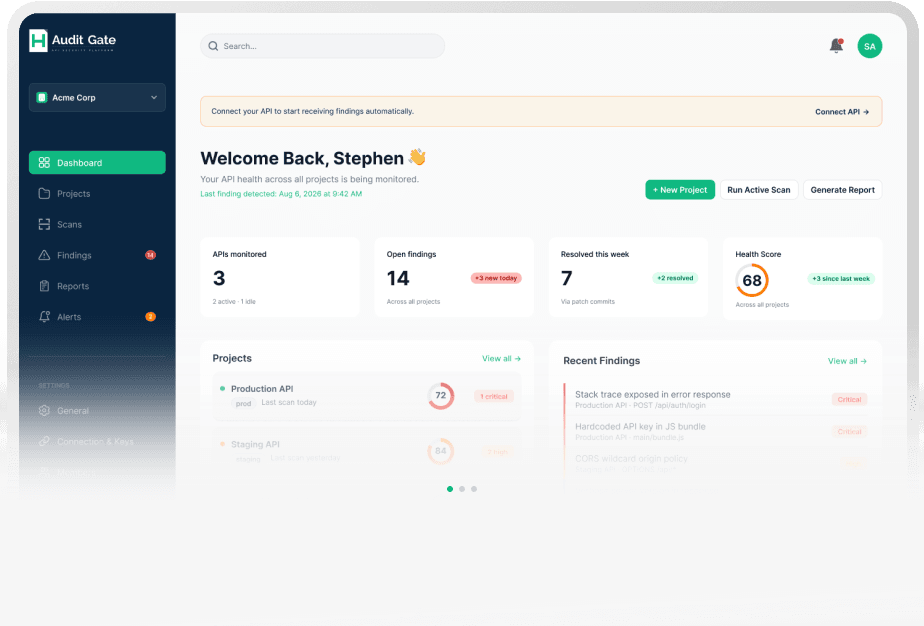
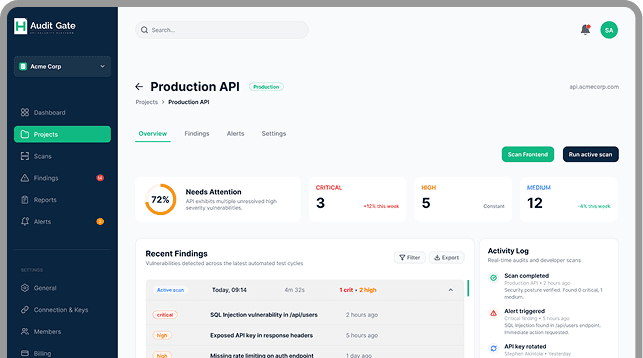
Every project carries a single score out of 100 that moves as findings are opened and closed, so you can see your security posture improving over time rather than guessing at it.
Full coverage. Zero blind spots.
Vulnerabilities caught the moment they happen.
Every API request routes through your AuditGate proxy. We analyze each one in real time, no agents, no SDK, no manual uploads. A critical finding surfaces within 30 seconds of the first vulnerable request.
- Findings appear within 30 seconds of detection
- 9 vulnerability categories checked on every request
- Evidence masked, raw tokens never exposed in UI
- AI fix steps generated per finding, stack-specific
A single number that tells the whole story.
AuditGate calculates a 0-100 health score for every project after each scan weighted by severity, tracked over 30 days, and visible across your entire workspace dashboard. No spreadsheets. No guesswork.
- Score weighted by severity
- Trend indicator since last scan
- Per-project scores shown on workspace dashboard
- Score included in every PDF audit report
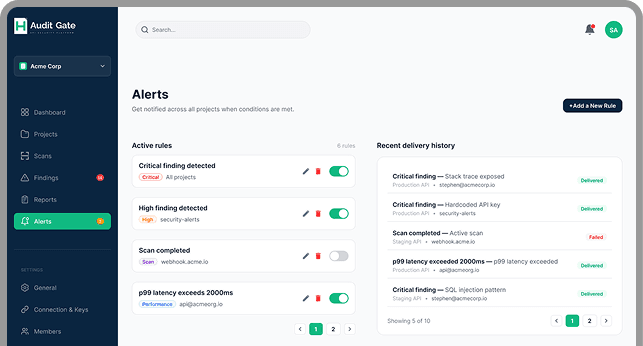
The right alert. The right channel. Right now.
Set rules once and AuditGate fires them the moment conditions are met, whether that's a critical finding, a completed scan, or a latency spike. Delivered to your inbox, Slack, or webhook within 60 seconds.
- Trigger on severity level, scan event, or latency threshold
- Toggle rules on/off instantly without deleting them
- Full delivery log with Delivered / Failed status per entry
- Score included in every PDF audit report
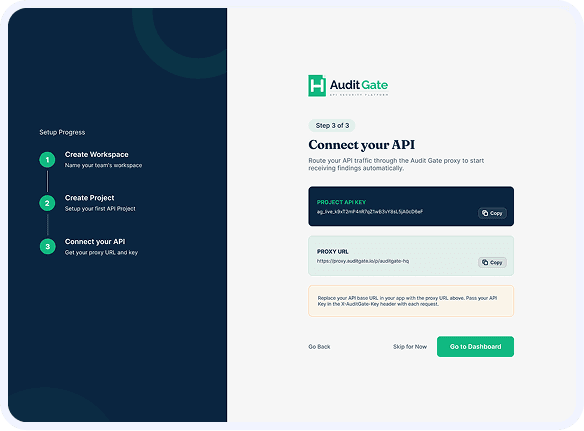
Connect your APIs
Simply import your OpenAPI/Swagger schema files or paste your core endpoint URLs. No code changes required.
Run automated scans
Trigger deep architectural scanning manually or configure them to execute automatically with every staging deploy.
Fix and verify
Receive copy-pasteable remediation snippets, patch instructions, and re-scan instantly to guarantee protection.
Plans for every team
You get the full security engine from day one, even on the free plan. Upgrading just means more projects, more seats, and more breathing room.
Free
Perfect for solo developers exploring API security.
- 1 workspace
- 1 project
- Solo only (1 seat)
- 50,000 requests/mo
- 7-day findings retention
- 1 active scan/day
- Email alerts only
- 1 alert rule
- PDF reports
- GitHub integration
- API access
Developer
For developers who ship APIs and need continuous security coverage.
- 1 workspace
- 3 projects
- 3 team members
- 500,000 requests/month
- 30-day findings retention
- 10 active scans/day
- Email + Slack alerts
- 5 alert rules
- 5 PDF reports/mo
- 1 GitHub repo
- API access
Startup
For growing teams that need compliance, unlimited scans, and full audit trails.
- 3 workspaces
- 10 projects
- 10 team members
- 2M requests/month
- 90-day findings retention
- Unlimited active scans
- Email + Slack + Webhook
- Unlimited alert rules
- Unlimited PDF reports
- Unlimited GitHub repos
- NDPC compliance report
Enterprise
Unlimited everything, dedicated support, custom contracts, and full compliance.
- Unlimited workspaces
- Unlimited projects
- Unlimited team members
- Custom request volume
- Custom retention (up to 1yr)
- Unlimited scans
- All channels + Custom
- Unlimited alert rules
- Full NDPC compliance
- Dedicated onboarding
- Dedicated support + SLA
- Custom invoicing


Integrates with your stack
No agents to install. No libraries to import. Point your base URL at our proxy and AuditGate handles the rest
Get Started for FreeTrust and security at AuditGate
We are asking you to put our software in front of the thing you are trying to protect. That is a significant request and it deserves a complete answer rather than a reassuring sentence. Everything below describes what actually happens to your data.
What we Inspect
Request and response metadata, headers, status codes, endpoint paths and response structure.
What we do not store
Request and response bodies are analysed in memory and discarded. We do not retain your customers' personal data or the contents of your payloads.
Redaction
Values matching known secret and token patterns are redacted before a finding is written to storage.
Retention
Findings and reports are retained according to plan, from 7 days on Free through to 180 days on Startup. Enterprise retention is configurable.
Access
Only the members you invite to a project can view its findings.
Deletion
Delete a project and every finding and report associated with it is removed with it.
Frequently Asked Questions
Your API is live. Is it secure?
You spent months on the API. Don't leave the door open. AuditGate takes 90 seconds to connect and immediately starts watching every request, every endpoint, every bundle.